01
Separate cryptographic boundaries
Your Vault and your Emergency Safe have separate keys and separate ways to unlock, not just labels or folders.
PasswordFix is in development. Features and timing may change before release.
PasswordFix is being designed around independent vault keys, device-scoped authorization, and explicit recovery boundaries.
Read the security approach →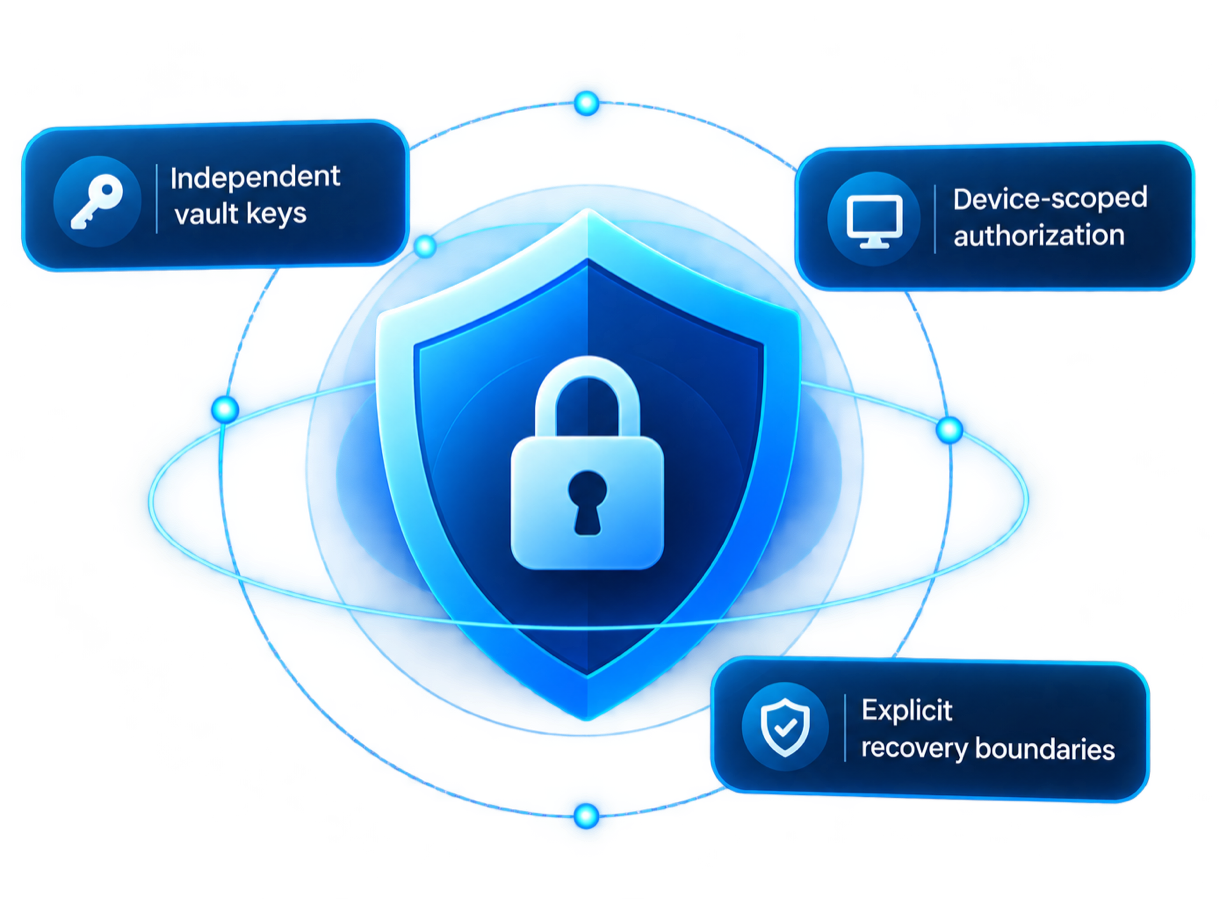
01
Your Vault and your Emergency Safe have separate keys and separate ways to unlock, not just labels or folders.
02
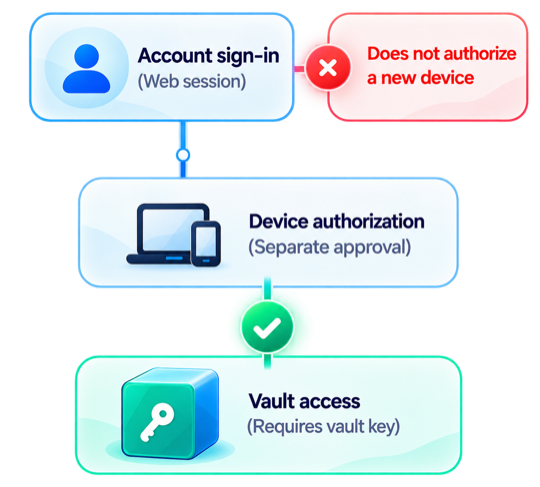
Signing in to our website never unlocks your data, and can't add a new device on its own. We'll never ask for your master password or PasswordFix Key by email, phone or chat.
03
Proving who you are can never replace missing keys.
They're encrypted on your device with keys we never have. What we can see: account details we need to run the service, such as your email address and the devices you add. Never what's inside your Vault or Emergency Safe.
Security claims will be updated as implementation and external assessment are completed.

Defined
Independent vault keys, device-scoped authorization, and explicit recovery boundaries.

In progress
Core architecture and security controls are being implemented.

Planned
Each major version of PasswordFix will be independently security reviewed and penetration tested before release.

Planned
Security claims will be kept up to date as new information becomes available.